From panic to plan: exposure management for the next PHP

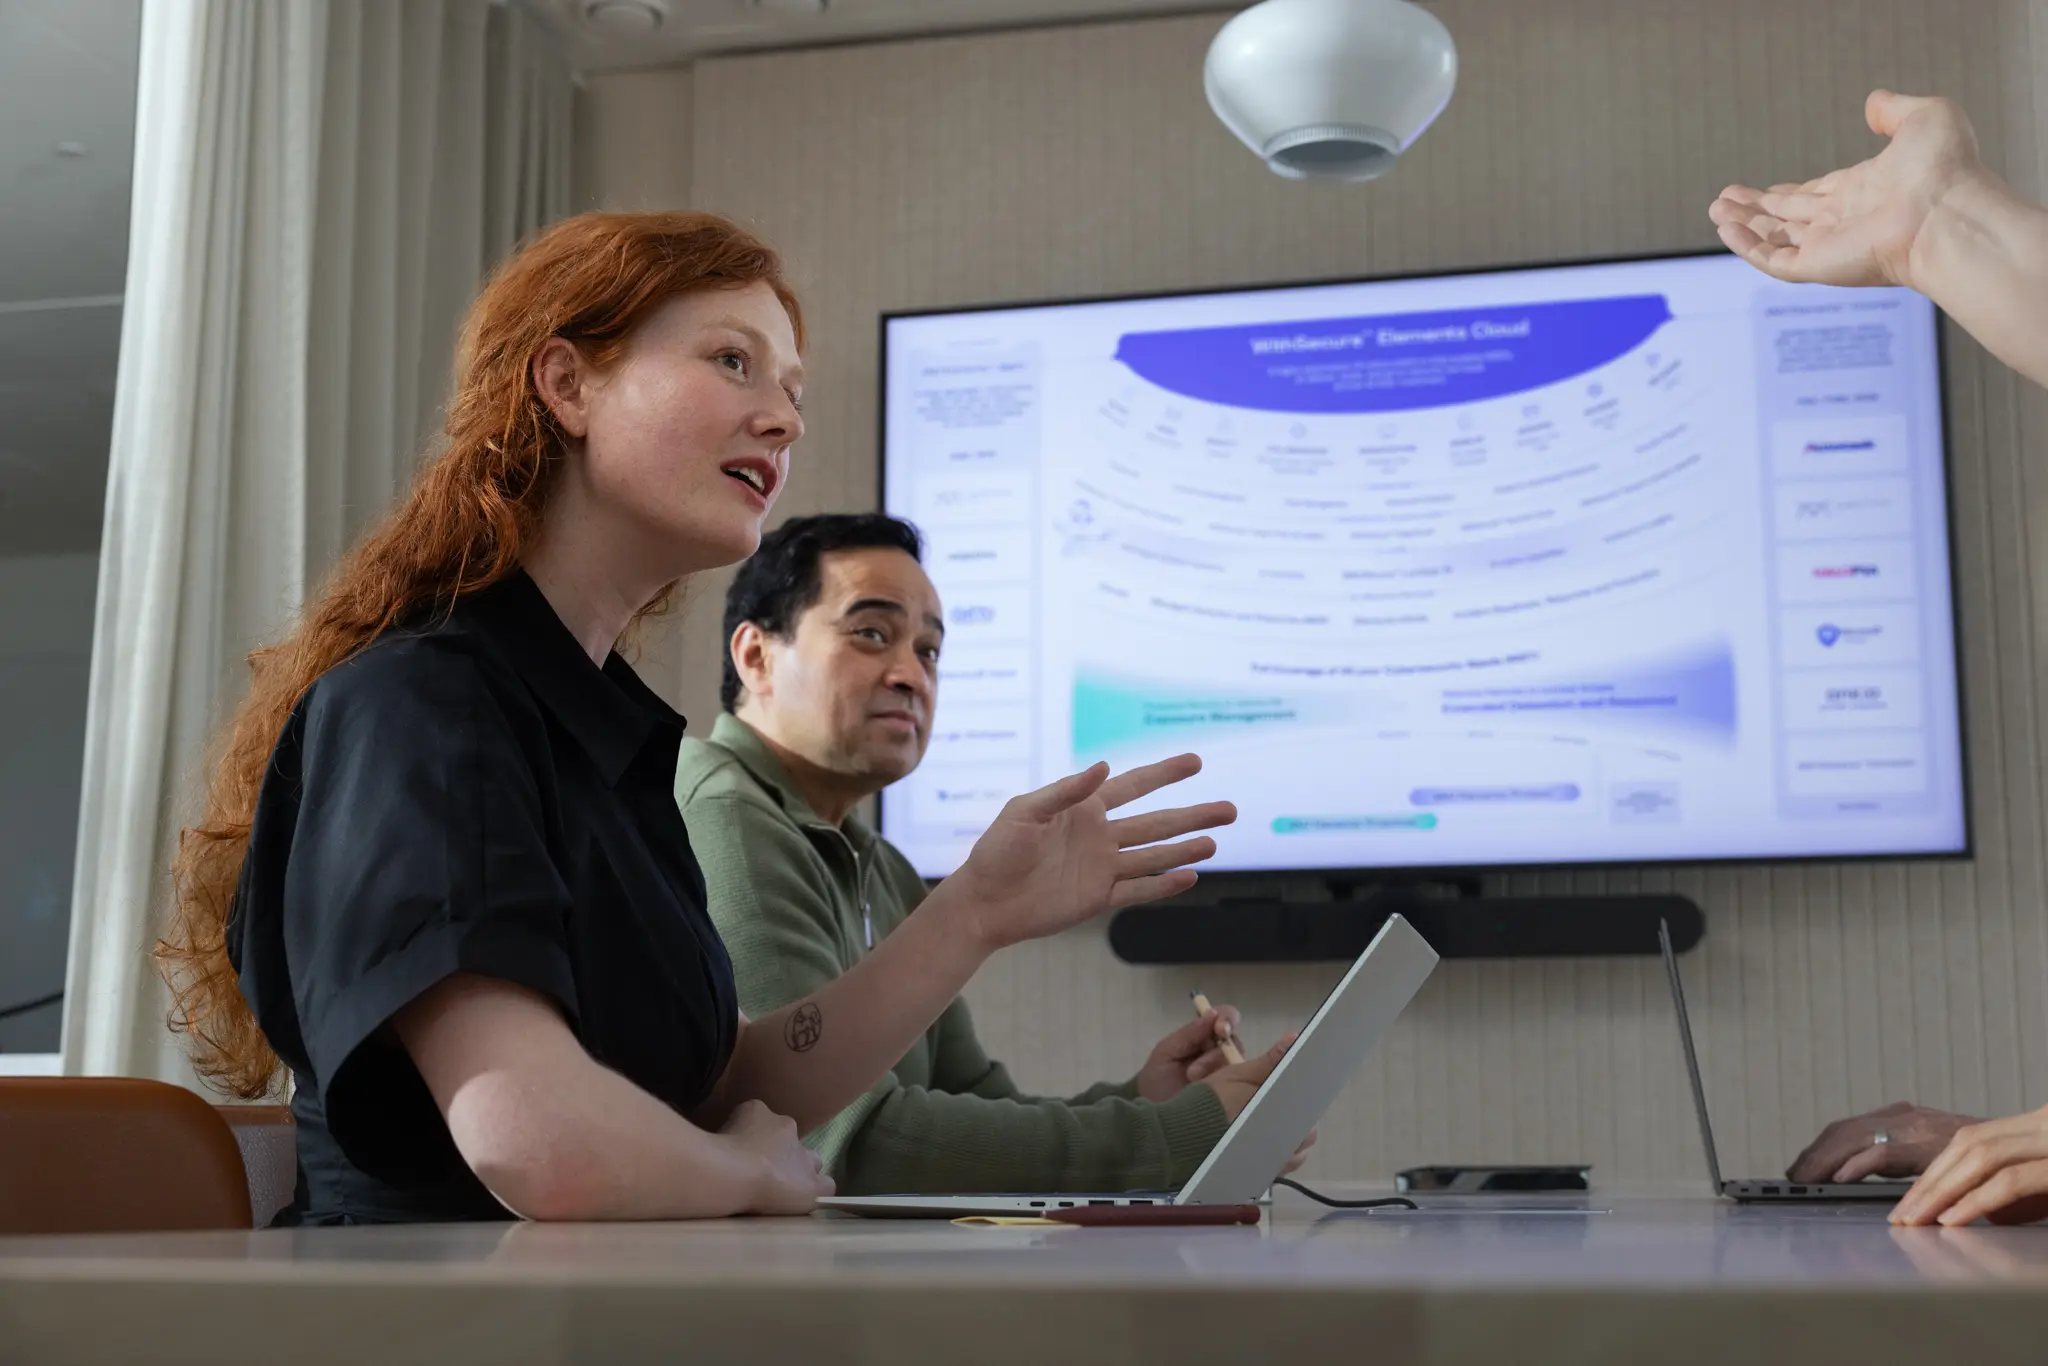
A woman with long red hair gestures while presenting beside a seated colleague, in front of a wall screen showing the WithSecure Elements Cloud architecture diagram.

There will be another PHP2Shell. It might be Java. It might be OpenSSL. It might be a library no one on your team has heard of.

The flaw changes. The first questions do not: What do we have? Is it affected? What is exposed? What goes first?

What exposure management does

WithSecure™ Elements Exposure Management (XM) gives you continuous visibility into exposures across on-premise assets, cloud services and digital identities. It helps you answer those questions before the advisory is a day old:

  • Find the assets. Including the ones nobody listed.
  • Identify vulnerable versions. So you know what is affected, not just what might be.
  • Prioritize by exposure. By exploitability, attacker motivation and business impact, not by CVSS alone.
  • Show it per partner. A clear view for each client, ready to share.

What it means for your MSP

One view across all your partners. A fast impact assessment when an advisory lands. A report you can hand to a partner without rebuilding it in a spreadsheet.

That is the difference between a scramble and a plan. You stay the hero. We stay the safety net.

What next?

Discover WithSecure™ Elements Exposure Management.
– No credit card required. No obligations.No complexity.

Blog post

Read our latest blogs
Blogi

Product

A critical PHP flaw is in the news. Here is what it means for your business.

Blogi

Product

72 hours of PHP2Shell: what MSPs learned

Blogi

Product

The SMB nightmare that ran on PHP