


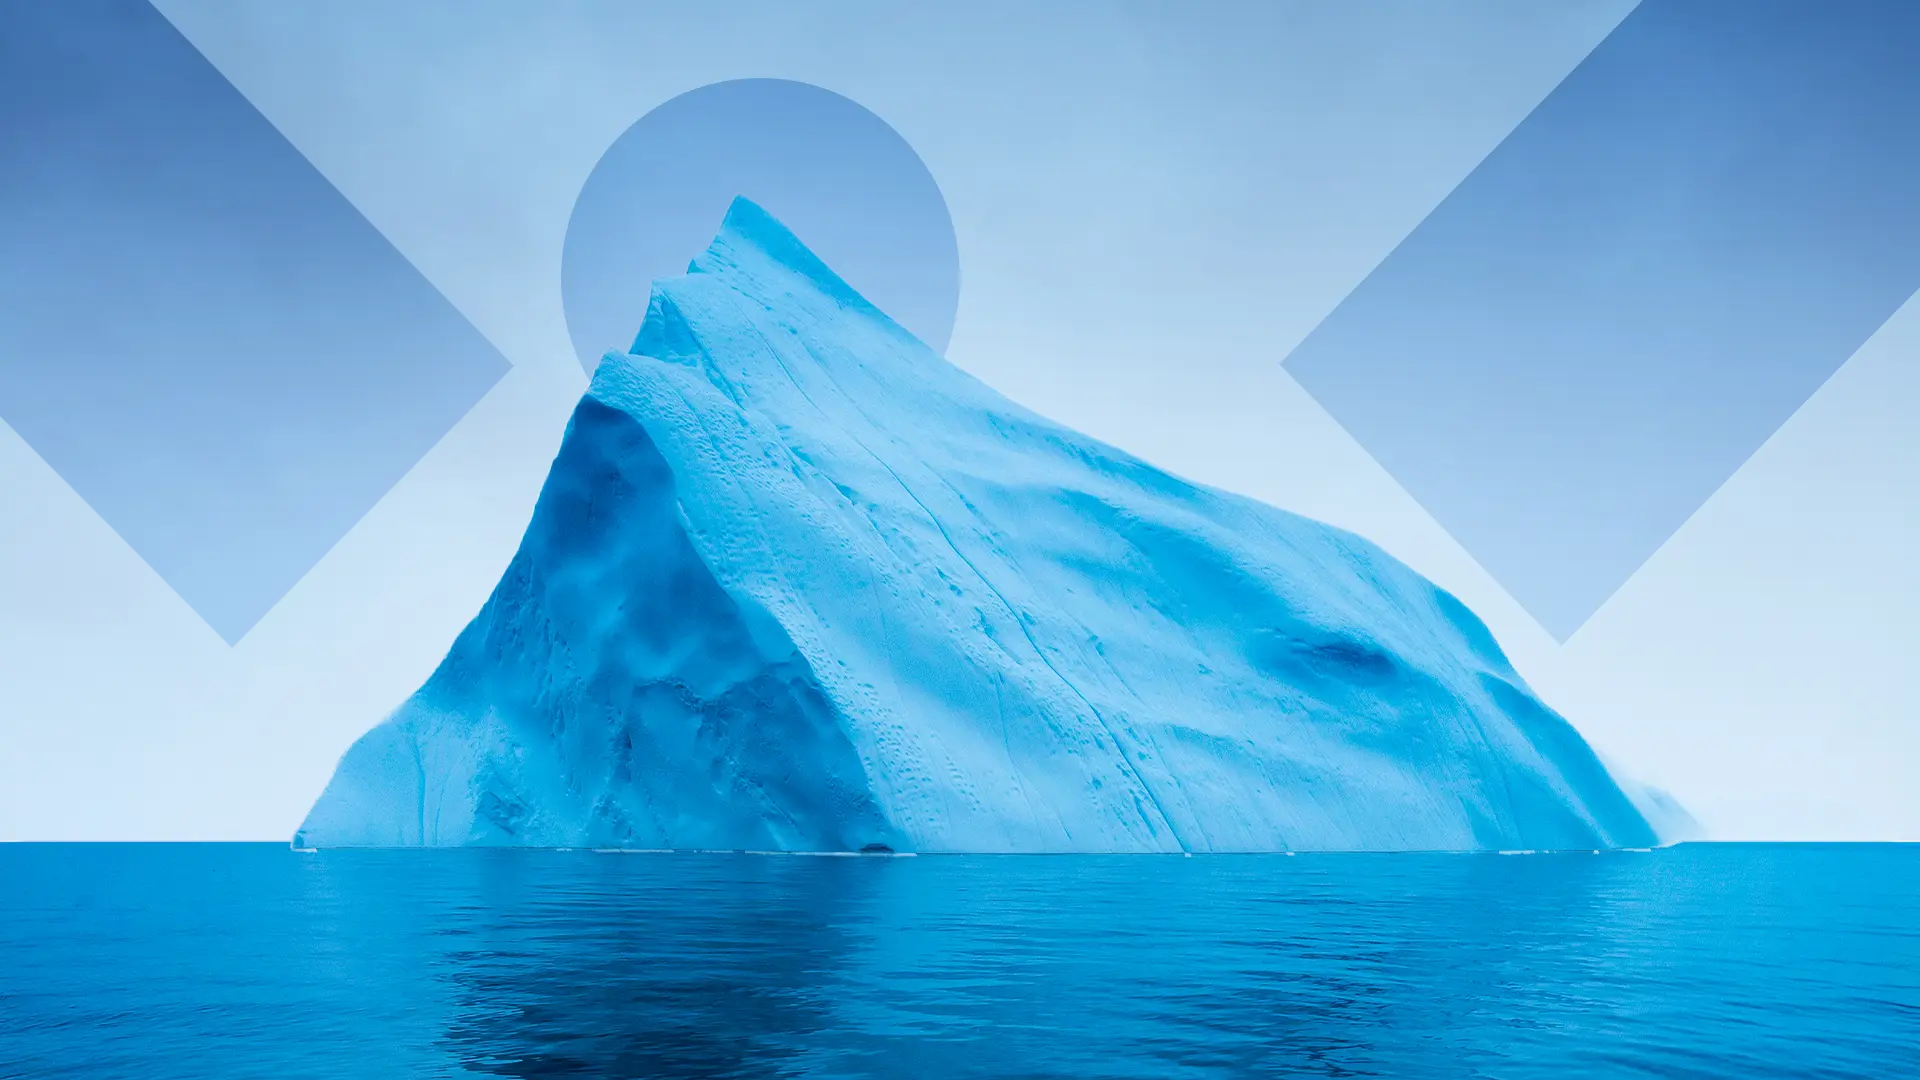
Shadow AI security means finding and governing the AI tools, assistants, extensions and agents that employees use without IT approval. Most companies have a bigger AI footprint than their IT team can see, and data can leave through every unmanaged channel. A simple framework helps: see what AI is in use, control what’s allowed, protect against misuse, and prove it with reporting.
Key takeaways
✓ More than 45% of employees are reported to use AI, and a lot of that use sits outside IT’s view.
✓ Security and risk concerns are reported as the number one barrier to scaling AI programs.
✓ Companies with a structured cybersecurity program see AI initiatives move about 20% faster.
✓ See, control and protect, then prove gives MSPs a conversation starter and a service roadmap.
Introduction
Every company has an AI transformation program. Some planned theirs. Many didn’t.
A finance team runs a report through a public chatbot. A sales executive installs an AI browser extension that IT never approved. A project team adopts a software tool with generative AI built in. The train, as WithSecure’s Suvi Silvanto put it at a recent MSP event, has already left the platform.
Your clients feel this, even if they phrase it differently: „I don’t know what my employees are doing with AI, but I know they’re using their personal assistants. Are we safe? Are we leaking data?“
This article gives you a plain framework to answer those questions and turn them into a managed service.
In this article, you’ll learn:
- What shadow AI is and where it hides
- Why security is holding AI programs back, and how to change that
- A four-step framework for securing AI in mid-sized companies
What is shadow AI, and why is it a security risk?
Shadow AI is any use of AI tools, assistants, plug-ins or agents that sits outside the organization’s approved and monitored environment. It’s a risk because data, credentials and decisions pass through channels that nobody governs.
We call the picture an „AIsberg.“ Above the waterline sits what IT can see: sanctioned tools and official rollouts. Below it sits a much larger mass:
- Personal AI assistants used for work tasks.
- Browser extensions with broad access to pages and data.
- Software with embedded generative AI that arrived through a routine update.
- AI agents that may hold more privileges than the human users who launched them.
The concern is data leaving through these channels. It’s also the question of who, or what, has permission to do what. An agent with wide access and no oversight is an identity problem as much as an AI problem.
Key points
- Usage is uneven. In some firms two people produce reports for everyone, while others already run AI inside their processes.
- Either way, every company needs visibility, guardrails and governance.
- AI security is becoming a discipline of its own.
Why is security the barrier to scaling AI?
Security concerns slow adoption
Leaders want the productivity and growth AI promises. Teams across the business are exploring how to apply it. Yet security and risk concerns are reported as the leading barrier to scaling AI programs. It isn’t a lack of ambition or budget. It’s a lack of confidence.
Structure speeds things up
Companies that put a structured cybersecurity program in place move AI initiatives about 20% faster. Clear rules and visibility remove the hesitation. Teams know what’s allowed, so they can start.
Security can’t be the bottleneck. It can be the reason a company moves with confidence.
That’s what your clients are really asking for, even when they don’t say it: confidence that they can start an agentic process somewhere, and that they’re safe when they do.
How do you secure AI usage? The see, control, protect, prove framework
Use these four steps as a conversation guide. Each step may involve a different person at the client.
- See: what AI is being used? Find out which tools are running, who uses them, with what permissions and credentials, and what data they touch. Include the sanctioned and unsanctioned. This step alone builds confidence, because it replaces guesses with a concrete picture.
- Control: what is allowed? Define policies. Which tools are approved? What data can go where? What can an agent do on its own? Control means clear rules, written down and enforced.
- Protect: how do we defend the business? Put guardrails in place and prepare dynamic, fast response. If an agent behaves unexpectedly or data starts to leak, the response should be quick and automatic where it can be.
- Prove: can you show it? Report on risk and posture continuously. Show leadership and auditors that the environment, AI and traditional IT alike, is under control. Proof turns security work into something the business can see.
The framework works because it’s simple. A CEO, an IT lead and an AI transformation team can each find their question in it.
Common challenges and solutions
| Challenge | Solution | WithSecure approach |
|---|---|---|
| IT can’t see personal assistants, extensions or embedded AI | Run an AI discovery and risk assessment | Start with visibility across identities, cloud and endpoints in a unified platform |
| Agents hold broad privileges | Treat agents as identities with least-privilege access | Identity and cloud security alongside endpoint protection show who and what has access |
| Policies exist on paper only | Pair policy with technical guardrails | Proactive security links detection, exposure and response so rules are enforced, not just written |
| Leadership wants evidence | Report posture and risk continuously | Risk reporting built for business conversations |
Frequently asked questions
Q: What is shadow AI? Shadow AI is the use of AI tools, such as personal assistants, browser extensions, embedded generative AI features and agents, without IT approval or oversight. It creates blind spots where data, credentials and permissions are unmanaged and may leave the organization.
Q: How common is AI use among employees? Reports indicate more than 45% of employees use AI. The figure varies widely. Some companies have a couple of people using AI for reporting, while others have AI embedded in their processes. Every company still needs visibility and governance.
Q: How do you secure AI in a company? Start by seeing which AI tools, users and permissions exist. Then define what is allowed, protect with guardrails and fast response, and prove control through continuous reporting. This see, control, protect, prove model works for both AI and traditional IT.
Q: Does AI security slow down innovation? It shouldn’t. Security concerns are currently the top reported barrier to scaling AI, while companies with structured cybersecurity programs move AI initiatives about 20% faster. Clear rules and visibility give teams confidence to proceed.
Conclusion
AI is already inside your clients‘ organizations. Some of it is approved. A lot of it isn’t.
You don’t need to start with a large program. Start by showing what’s below the waterline. Then work through control, protection and proof. That path builds confidence for your clients, and it builds a service for you.
Watch now: Proactive Security in the AI World: How MSPs Build New Services
Blog post
Read our latest blogs
Blog
Blog
Proactive Security: How MSPs can keep up with a 29-minute attack
Blog