What is IoT security?
IoT security is the practice of finding, protecting and monitoring every internet-connected device in your organisation, from cameras and sensors to building controls and refrigeration. Most of these devices are rarely patched, sit outside IT’s view and are often exposed to the internet. The fix is visibility, reduced exposure, continuous monitoring and a rehearsed response.
Key takeaways:
- Connected devices are now a major part of the attack surface, and many are unmanaged.
- Older devices may no longer receive security updates, so they must be isolated or replaced.
- Remove unnecessary internet exposure and put remote access behind multi-factor authentication.
- Detection speed decides the damage: monitor settings and alarms around the clock.
Introduction
Most organisations now run far more connected devices than they have laptops: cameras, badge readers, printers, building controls, sensors, and refrigeration and industrial equipment. Each is a small computer on your network, and each is a potential way in. That is why IoT security, the discipline of protecting these devices, has become a core part of cyber risk management.
The Internet of Things (IoT) is where many security programmes have their biggest blind spot. These devices are installed once, expected to run for years, and rarely get the attention given to servers and endpoints.
In this article, you will learn:
- Why IoT devices are hard to secure
- How attackers exploit them, with a recent real-world example
- Eight practical steps to secure connected devices
Why are IoT devices hard to secure?
IoT devices are hard to secure because they are rarely patched, often unmanaged, and built to run for many years. The same weaknesses appear whatever the device does.
Patching and lifespan
Many devices receive few updates, and older ones may receive none, so known vulnerabilities stay open for good. A device built ten years ago was designed for reliability, not for today’s threat landscape. Securing it may mean changing connectivity, adding network equipment or replacing it, which is a budget decision, not a quick fix.
Ownership and visibility
Devices are often bought and managed by facilities, operations or a contractor. As a result, they never appear in the IT asset inventory, vulnerability scans or monitoring. If you cannot see a device, you cannot protect it.
Weak defaults and open remote access
Default or shared passwords, unencrypted protocols and missing multi-factor authentication are common. Remote access added for convenience, often by a third party, is forgotten and ends up exposed to the internet.
How do attackers exploit IoT devices?
Attackers find exposed devices with simple internet scanning, then try default credentials or known flaws. Once in, they can change settings, disable alarms, disrupt operations, steal data, or use the device as a foothold into a poorly segmented network. Compromised devices can also be recruited into botnets and used against others.
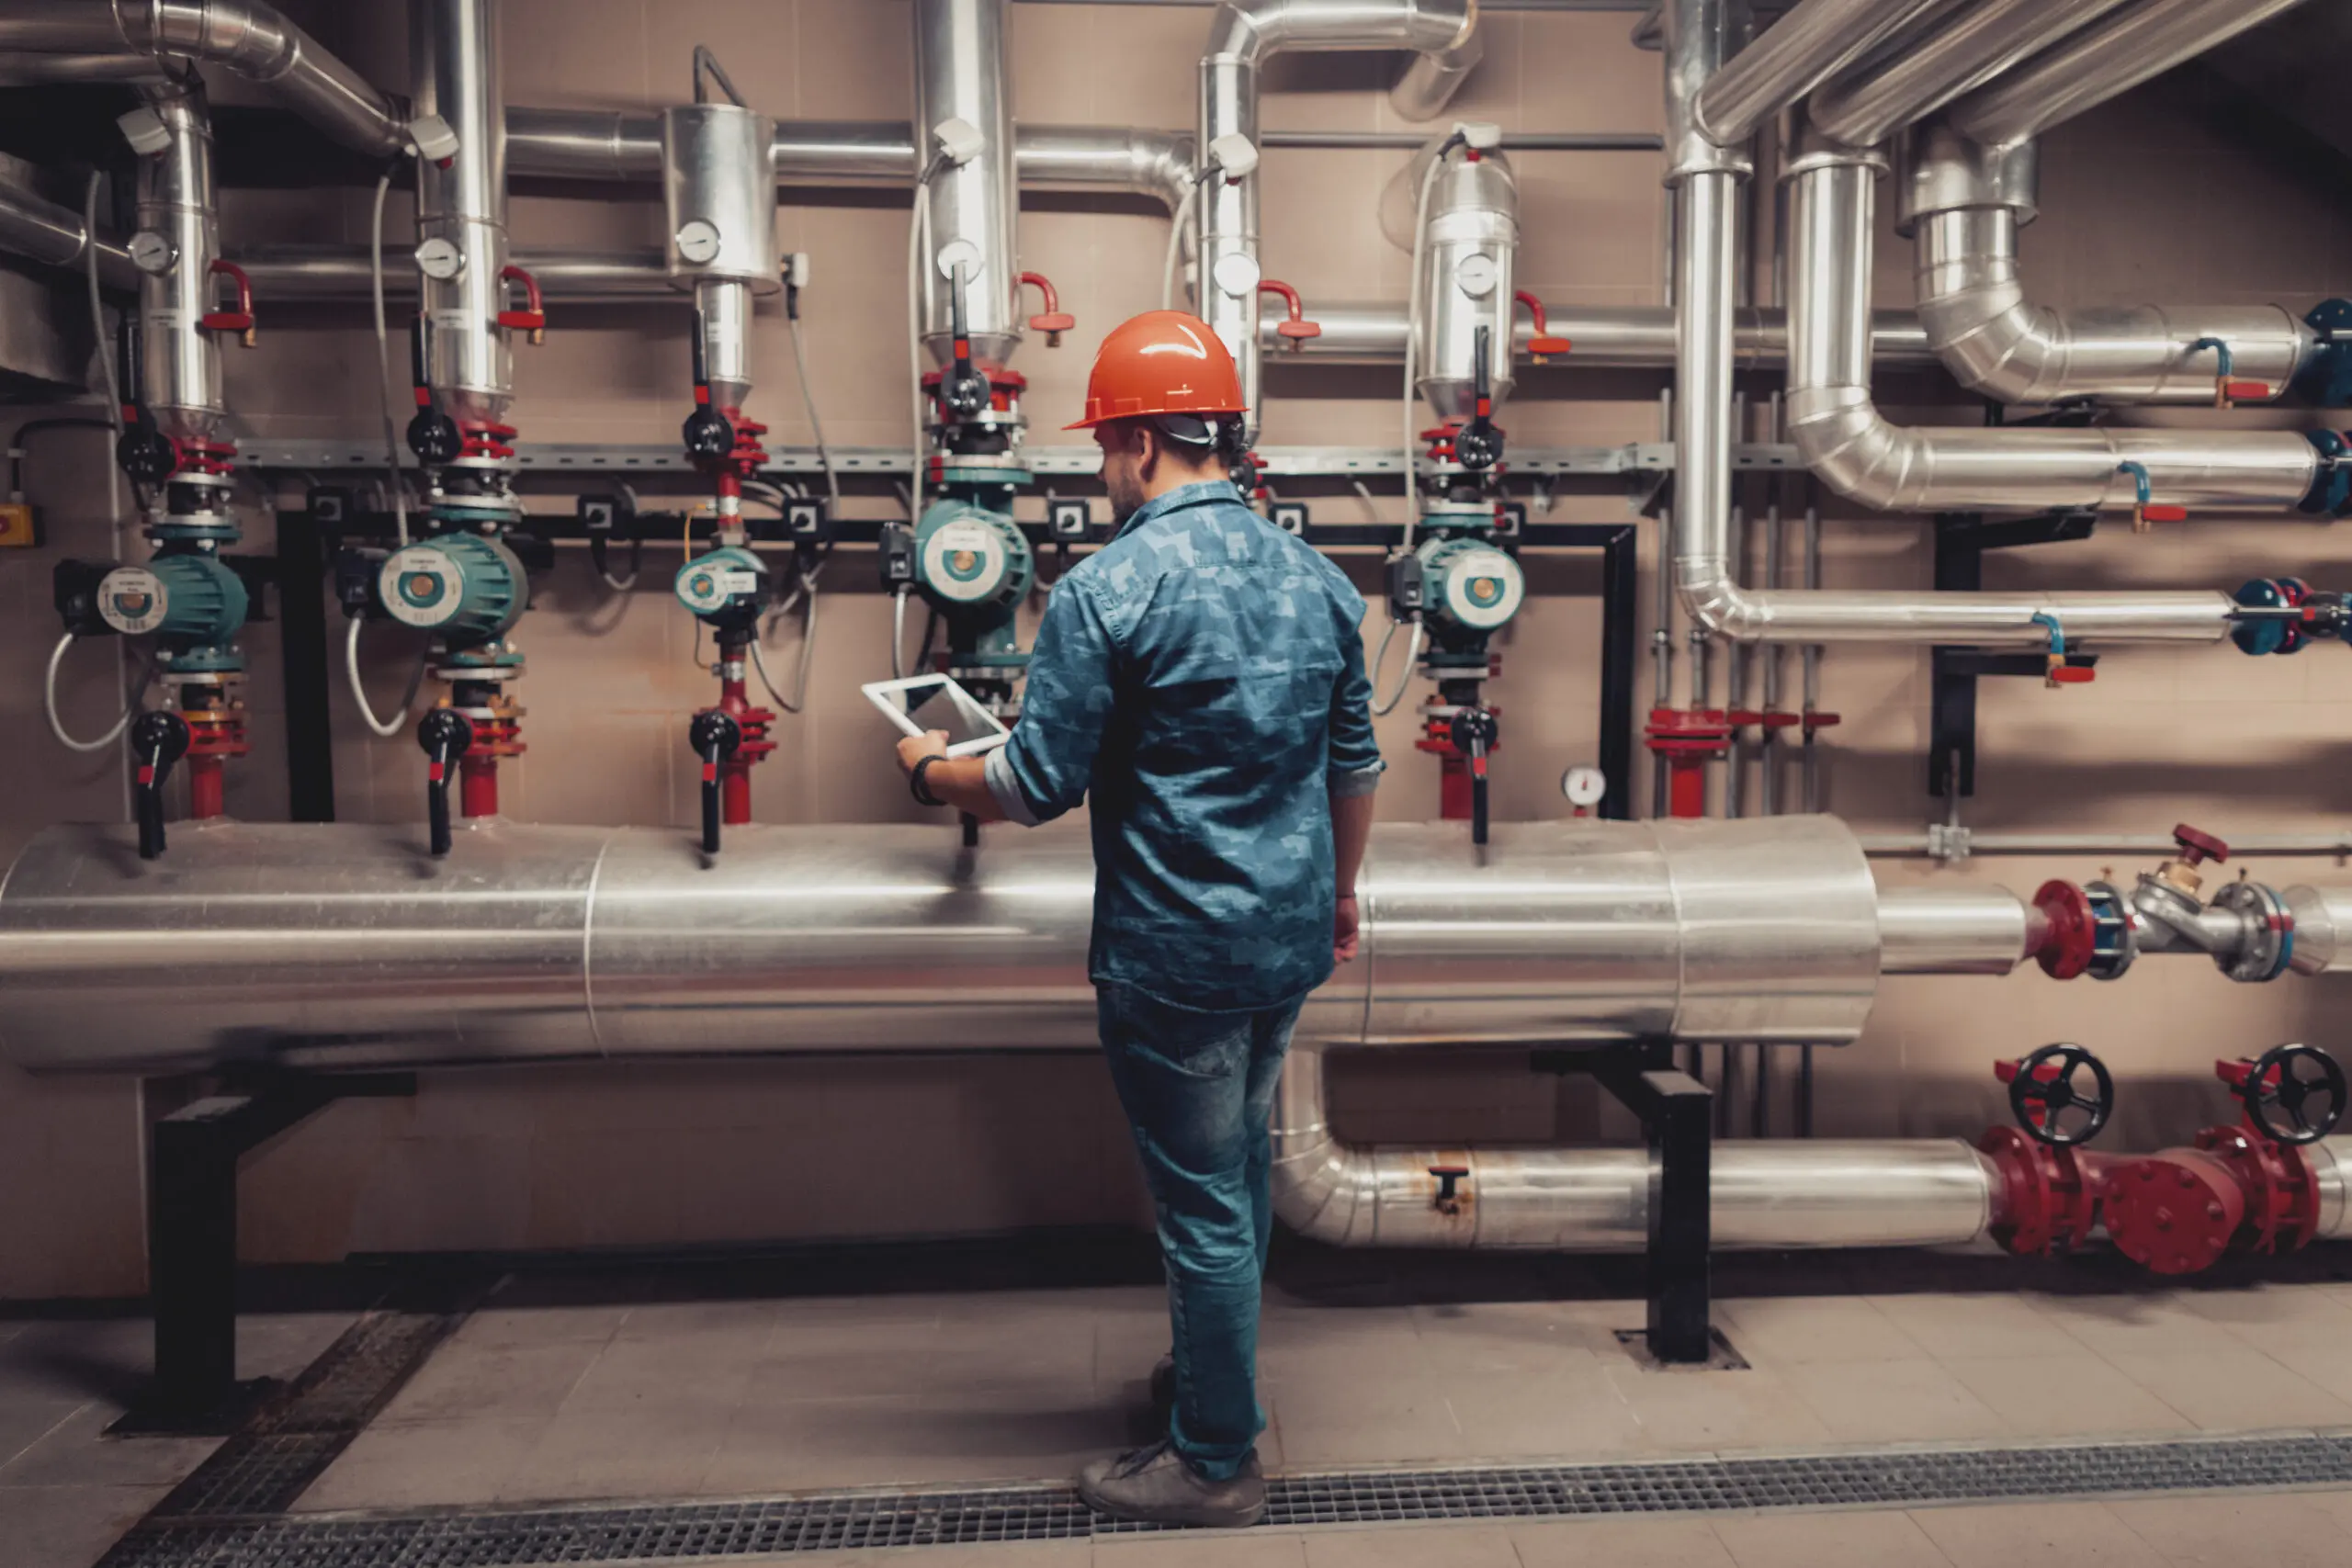
The impact depends on what the device controls. A camera leaks footage. A building controller affects comfort and safety. A device that controls something physical, such as temperature, access or machinery, can cause real-world harm and real financial loss.
A recent example: refrigeration controllers
Incidents affecting refrigeration systems have been reported across Europe, and France’s CERT-FR has separately warned of numerous compromises involving refrigeration controllers. In Estonia, attackers reportedly set a grocery store’s refrigeration to +50 °C, and the activity was detected and stopped within around ten minutes.
The timing and geographic spread deserve attention, but they do not establish that the incidents are connected or used the same access method. Whether they share a vulnerability, cause or actor needs further evidence, so conclusions on attribution or motive would be premature. The operational lesson holds regardless: exposed, unsupported controllers are an easy target, and speed of detection decides the damage.
How do you secure IoT devices? Eight steps
The steps are the same for any IoT estate. Start with visibility, then reduce exposure, then monitor and rehearse.
- Find every connected device. Build an inventory that includes devices managed by facilities and contractors. Record make, model, firmware, location and owner.
- Check support status. Confirm whether each device still gets security updates, and plan for the ones that do not.
- Remove unnecessary internet exposure. Review who can connect remotely and how. Put remaining access behind a VPN or secure gateway with multi-factor authentication and individual accounts.
- Change defaults and segment. Replace default credentials and keep IoT devices on separate network segments from corporate and payment systems.
- Verify configuration. Record a known-good baseline for critical settings such as setpoints, schedules and alarm thresholds, and check against it.
- Monitor continuously. Alert on configuration changes, disabled alarms, new remote sessions and unusual behaviour, and send alerts to someone who can act outside office hours.
- Assign ownership and rehearse. Decide who owns each device class, who gets the alert and what happens in the first ten minutes. Then test it.
- Plan for end of life. Where a device cannot be secured, set a date for added controls or replacement.
Common IoT security challenges and solutions
| Challenge | Solution | How WithSecure helps |
|---|---|---|
| Unknown devices on the network | Continuous asset discovery and a shared inventory | Attack surface visibility and exposure management |
| Unsupported or unpatchable devices | Isolate, restrict access, then replace on a set date | Prioritised risk view to decide what to fix first |
| Nobody watching outside office hours | 24/7 monitoring with a clear escalation path | Managed detection and response |
Frequently asked questions about IoT security
What is IoT security?
IoT security protects internet-connected devices, such as cameras, sensors and building controls, from unauthorised access and misuse. It combines asset discovery, secure configuration, network segmentation, access control and continuous monitoring, because many IoT devices cannot run traditional endpoint protection.
Why are IoT devices a target for attackers?
IoT devices are attractive because they are often exposed to the internet, use default passwords, and rarely receive updates. They also sit outside normal IT monitoring, so attackers can use them to change settings, disrupt operations or reach other systems without being noticed for hours.
How do I know which IoT devices I have?
Start with network discovery and ask facilities, operations and contractors what they have installed. Record make, model, firmware, location and owner for each device. Repeat the exercise regularly, because new devices are added all the time, often outside IT’s knowledge.
What should I do about IoT devices that no longer get updates?
Remove their internet exposure, place them on an isolated network segment, restrict and monitor remote access, and set a replacement date. Some devices can only be secured through changed connectivity, extra network equipment or replacement, so budget for it early.
Conclusion: pass the 02:00 test
Imagine one of your devices is tampered with at 02:00. Would anyone know before morning? Where physical processes and food safety are concerned, even a few hours can have serious consequences.
Strong IoT security comes down to giving every connected device an owner, an update path, a monitored connection and a plan for when something unexpected happens. Attackers do not need to know what a device is for. They only need to find it.
Ready to see what is exposed in your environment? Talk to us about attack surface visibility and managed detection for your connected devices.