Most security teams can already see the AI tools they approved. What they can’t see is everything beneath that: personal AI assistants employees bring to work, AI browser extensions quietly requesting broad permissions, AI agents operating under their own unmanaged credentials, and GenAI features embedded inside everyday SaaS apps. Each layer is less visible than the one above it, and each one is growing faster than governance can track.
✓ Approved AI tools are the only part of the AI attack surface most security teams can currently see.
✓ Employees’ personal AI assistant accounts, used for work tasks on personal logins, sit entirely outside IT’s visibility.
✓ AI browser extensions often request page-level read and write access on every site an employee visits.
✓ Machine identities, including AI agents, are on track to outnumber human identities by more than 80 to 1. [1]
✓ GenAI features embedded inside everyday SaaS tools process company data without ever going through a separate approval step.
Picking up where we left off
Our first blog in this series looked at why AI security has become a board-level issue. Our second covered how WithSecure is starting to answer it, beginning with visibility into shadow AI and agentic identities. This blog makes the scale of that visibility problem concrete, using an image that keeps coming up in conversations with security teams: the iceberg.
The tip of the iceberg: approved AI tools
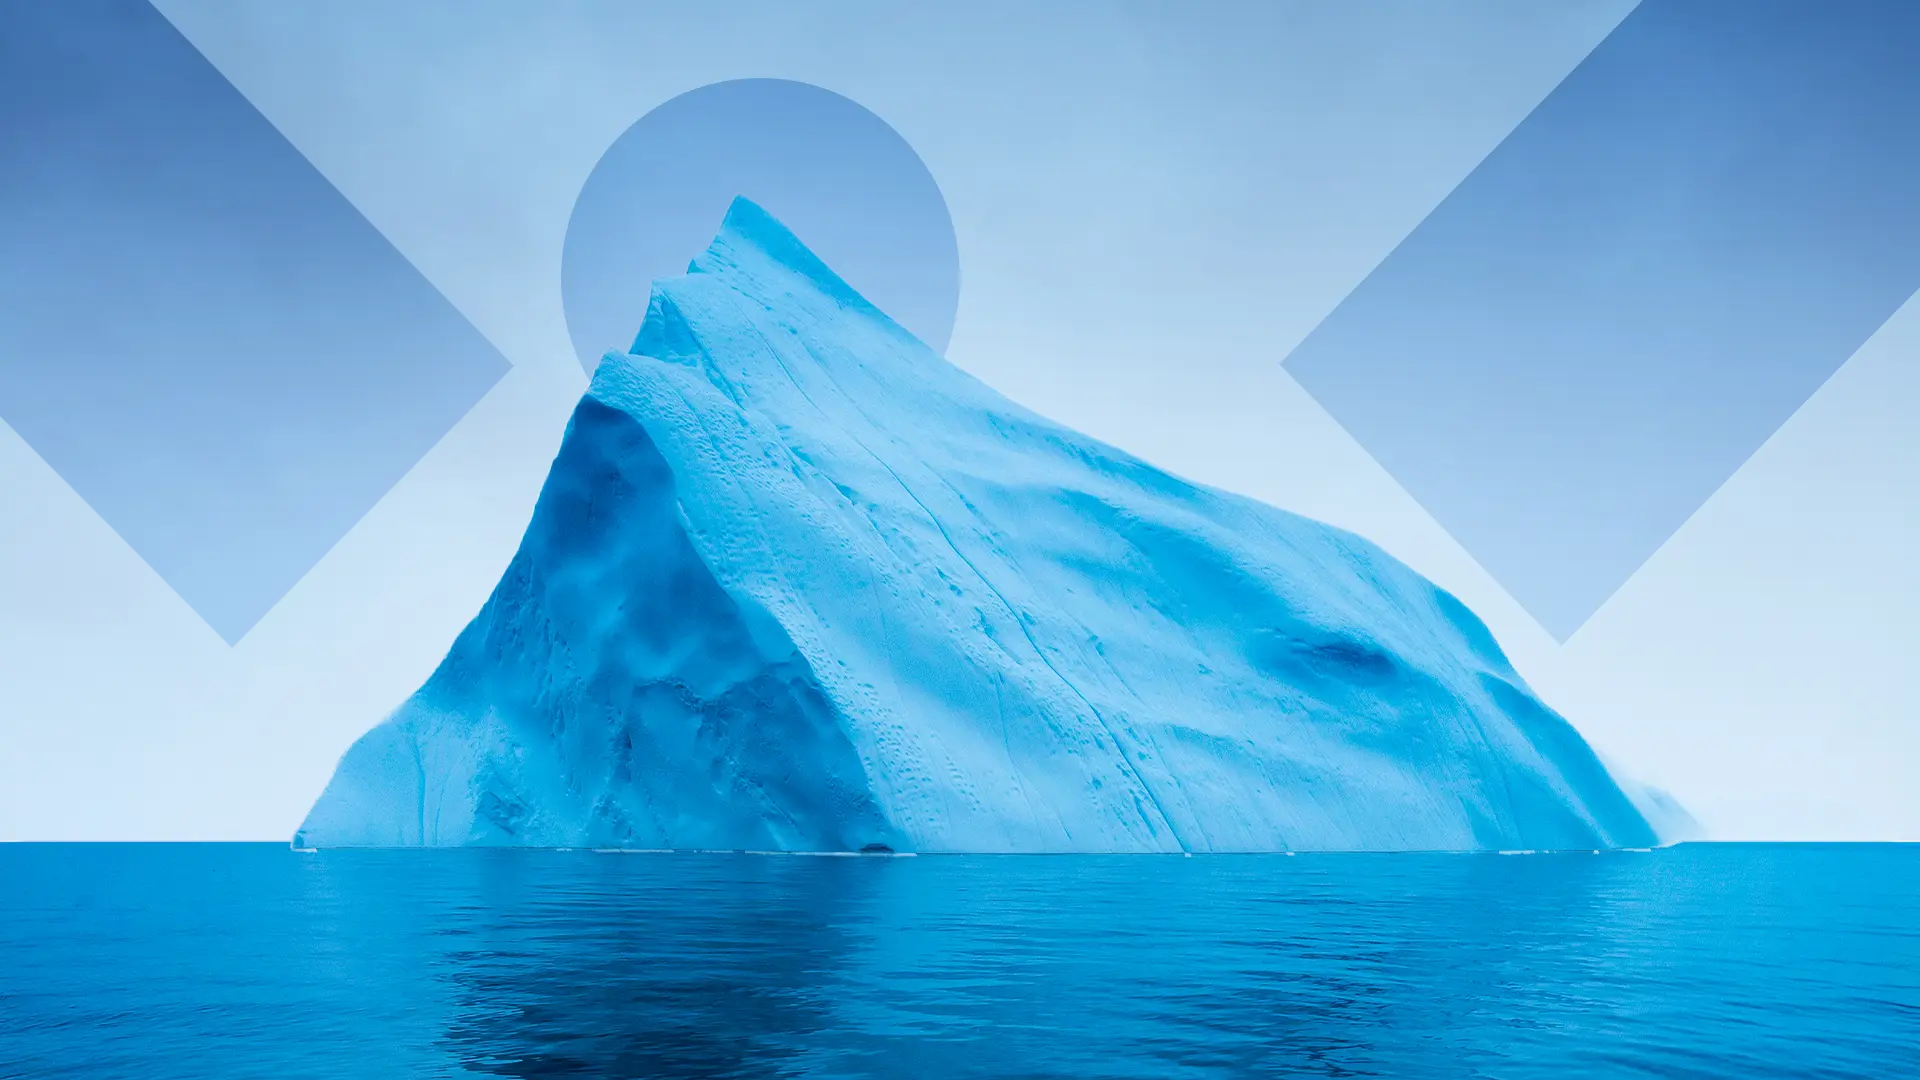
Ask most security teams what AI is running in their organisation, and they’ll point to what they approved: a named chatbot license, a Copilot rollout, maybe an AI feature in the CRM that procurement signed off on. That’s real, and it’s worth tracking. But it’s also the smallest and most visible part of the problem, the tip of the iceberg sitting above the waterline. Everything else is underneath, and it’s bigger than the part anyone can see.
Four layers hiding beneath the surface
Personal AI assistants
Employees don’t wait for an approved rollout. They sign up for a free or personal-tier AI assistant with their own email address and start using it for work tasks: drafting emails, summarising documents, writing code. None of that activity touches a corporate account, so there’s no audit trail and no device-level signal that would normally flag it. It’s the most common layer and the hardest to see, because it looks, from the network’s perspective, like an employee simply browsing the web.
AI browser extensions
Sidebar AI tools, the kind that add a chat panel to every page a person visits, are popular precisely because they’re easy to install and hard to police. Many request broad permissions just to function, including the ability to read and change data on every site visited. If an extension turns out to be malicious, or is compromised after installation, an attacker can use that same access to pull sensitive data, credentials, and proprietary code straight from the pages an employee works in. Traditional antivirus struggles here because these tools often load their payload dynamically from a remote server after installation, so there’s no file sitting on disk to catch.
AI agents and their credentials
Every new AI agent, coding assistant, or GenAI integration typically spins up its own credentials, tokens, or service accounts, most of which escape central tracking. These machine identities are already projected to outnumber human identities by more than 80 to 1, and agents often carry more standing privilege than the humans who built them. [1] Without visibility into what an agent can actually reach, that excess privilege becomes an unmonitored path for data exfiltration or lateral movement, the same risk as the browser-extension problem, just operating at agent scale.
GenAI inside SaaS apps
The deepest and least visible layer is GenAI that arrives already built into a tool the organisation already approved. A CRM gets an AI-assisted writing feature, a collaboration platform gets an AI meeting summariser, a help desk tool gets an AI-drafted reply suggestion. None of it requires a new procurement decision, because the parent application was already sanctioned.
Why the hidden layers matter more than the visible one
Only 41% of cybersecurity teams are involved in the planning phase of a generative AI rollout, and 89% of business technologists say they’d bypass cybersecurity guidance entirely if it stood between them and a business objective. That’s exactly how an iceberg grows underwater while the visible tip stays the same size: each new AI tool, extension, agent, or embedded feature adds mass below the surface long before anyone decides whether it belongs there.
| Hidden layer | What it looks like | Why it’s missed | What closes the gap |
| Personal AI assistants | Employees using their own ChatGPT, Claude, or Gemini logins for work tasks | No corporate account, no audit trail, no device-level signal | Shadow AI software view in software inventory, whether or not the tool was installed |
| AI browser extensions | Sidebar tools like ChatGPT’s extension or Perplexity requesting page-level access | Loads dynamically from a remote server, so there’s no file for antivirus to scan | Browser extension discovery plus Browsing Protection at runtime |
| AI agents & their credentials | Agents, coding assistants, and GenAI tools spinning up their own tokens and service accounts | Machine identities are on track to outnumber human ones by more than 80 to 1 | Visibility into AI and agentic identities via the existing Microsoft Entra ID integration |
| GenAI inside SaaS apps | AI features embedded in everyday platforms, processing company data as part of the core product | Never goes through a separate approval step, so it rides in on an already-approved tool | The next frontier: extending visibility from the tool itself to the AI capability inside it |
Frequently asked questions
What is the shadow AI iceberg?
It’s a way of visualising that the AI tools a security team has approved and can see are only a small, visible fraction of all the AI actually in use. Personal AI assistants, browser extensions, agent credentials, and embedded GenAI features make up the much larger, hidden majority.
What’s the difference between shadow AI and sanctioned AI?
Sanctioned AI has gone through procurement, security review, and a managed account. Shadow AI is anything used outside that process, from a personal chatbot login to an AI browser extension nobody asked IT about.
Why are AI agent credentials harder to track than human accounts?
Agents generate their own tokens and service accounts automatically, often with broader access than the person who configured them, and most organisations don’t yet treat agent identities with the same rigor as human ones.
Can blocking AI browser extensions solve the problem?
Blocking helps, but it only addresses one layer. Extensions are a known, visible-once-you-look-for-it problem; personal AI assistants, agent credentials, and embedded GenAI features each need their own kind of visibility.
Is embedded GenAI inside SaaS apps really a bigger risk than standalone AI tools?
It’s a harder one to see, which is often more dangerous in practice. A standalone tool at least triggers a procurement conversation. GenAI embedded inside an already-approved app rides in without one.
Start by looking below the waterline
None of these four layers are exotic or rare. They’re already present in most organisations today, just below a waterline most security tooling wasn’t built to see past. The fix isn’t a single control, it’s the same principle that applies to the visible tip: find it, then decide what to do about it.
Curious what’s sitting below your own waterline? Let’s take a look together.
Sources
[1] Forrester Global IAM Market Forecast, 2024 to 2029. January 2026.